Most organisations cannot say where their encryption actually is
Encryption sits underneath everything. Customer records, payments, contracts, internal messages, and every connection between your systems and your suppliers.
Almost none of it is documented in one place. And the algorithms most organisations rely on today will not survive a large enough quantum computer.
You cannot protect what you cannot see
Most organisations can name a few places they use encryption. Very few can produce a complete list, including third party connections, code libraries and the systems that quietly manage keys in the background.
The harvest has already started
Encrypted data is being collected today and stored until it can be opened later. It is known as harvest now, decrypt later. Anything that has to stay confidential beyond the next few years is already exposed.
This is not a software update
Becoming quantum safe means finding every use of cryptography, deciding what matters most, and migrating it. For an average organisation that is closer to a decade of work than a project.
One hour, and you will leave knowing what to do next
No sales pitch. Andy will walk through where quantum computing actually is, what it breaks, and the practical steps organisations are taking now.
The deadline is closer than the technology
The temptation is to treat quantum as a problem for later. The arithmetic says otherwise. Most governments have committed to being quantum safe by 2033. For an average organisation that migration is around ten years of work. Which means anyone starting today is already behind, and anyone who has not started is making a decision whether they realise it or not.
IBM co-created the first post-quantum cryptographic standards now adopted by NIST, and its Quantum Safe platform covers every layer from applications to network protocols. Northdoor brings the consultancy work that turns those tools into a plan your teams can actually deliver. As an IBM Gold Business Partner you get the full depth of IBM’s capability rather than a cut down version.
Stats:
- 2033, the deadline most governments have committed to
- Around 10 years, the migration effort for an average organisation
- 2035, when a machine capable of breaking today’s encryption is expected
A genuine expert, not a product demo
Professor Andy Stanford-Clark is an IBM distinguished engineer and leads IBM’s Quantum Ambassador team in the UK. He is joined by AJ Thompson of Northdoor, who works with the organisations that have to plan this migration and deliver it.
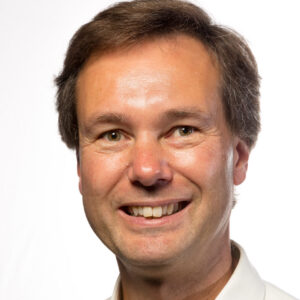
Professor Andy Stanford-Clark, IBM
Andy Stanford-Clark is an IBM distinguished engineer, a master inventor with more than 45 patents, and leads IBM’s Quantum Ambassador team in the UK. He specialises in Quantum Computing and Post-Quantum Cryptography. Andy is based at IBM’s Hursley Park laboratories near Winchester, and has been a renowned expert in Internet of Things technologies for more than 25 years. He has a BSc in Computing and Mathematics, and a PhD in Computer Science. He is an Honorary Professor at the University of East Anglia, a Visiting Professor at the University of Newcastle, an Adjunct Professor at the University of Southampton, and a Fellow of the British Computer Society.
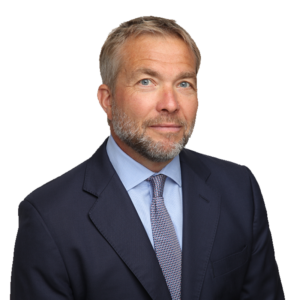
AJ Thompson, Northdoor
Chief Commercial Officer at Northdoor and a recognised voice in cyber security, data governance and cloud strategy. More than 25 years advising enterprise organisations, and a member of the IBM Worldwide Security Advisory Council.
Why quantum security needs attention now
Get a 90 day trial of IBM Quantum Safe
Everyone who attends gets 90 days with the IBM Quantum Safe platform, the same tooling used in our assessment. Long enough to run a real discovery across your estate rather than just look at a demo.
From a one hour webinar to a plan you can act on
If you want to know where your own organisation stands, the Northdoor Quantum Safe Assessment takes the same approach Andy describes and applies it to your estate.
Discover
We map every use of cryptography across your applications, systems, networks and third party connections, and produce your cryptography bill of materials.
Assess
We rank what we find by risk, by how long each secret needs to stay secret, and against the standards your sector will be held to.
Roadmap
You get a prioritised migration plan with clear next steps, plus a summary written for your board rather than your engineers.